A roundtable for the people who own security and compliance decisions
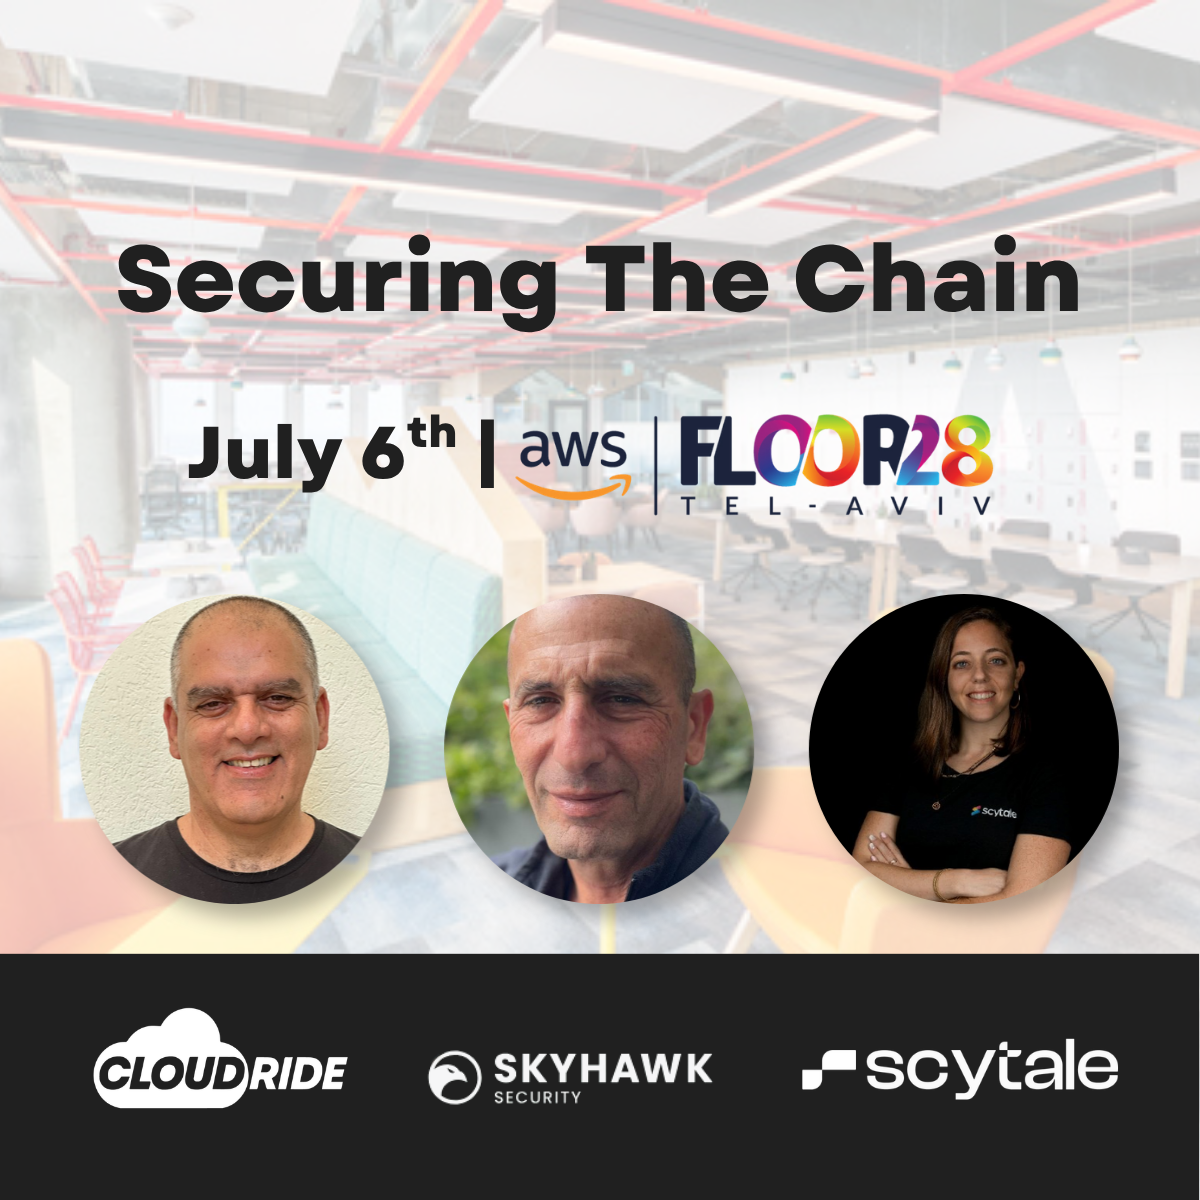
🗓️July 6th 10:00-12:00
📍AWS Experience at Floor 28
Derech Menachem Begin 121, Tel Aviv-Yafo
AI-driven attacks and third-party risk are growing faster than any once-a-year checklist can keep up with. Security, compliance, and governance can’t stay in separate silos anymore – this roundtable puts all three in one room.
Join leaders from Skyhawk Security, Cloudride, and Scytale for an intimate, no-fluff session on what risk readiness actually looks like for a growing company: how AI-based continuous security validation produces the evidence compliance requires, which standards move deals forward, and how smaller teams stay audit-ready – without an enterprise budget.
Built for CTOs, R&D leaders, and co-founders of startups and SMBs – small enough to ask the real questions, with the right people to answer them.
Save your spot today and walk out risk-ready:
Meet the Speakers
Adar Givoni
Director of Customer Services, Scytale
Lior Atias
Fractional CISO & DPO, Cloudride
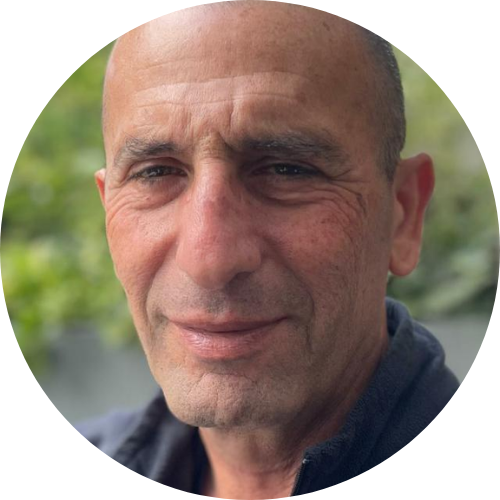
Noam Markfeld
VP Sales, Skyhawk Security
- In‑person meetup. Seats are limited.
Agenda
10:00 – 10:30 | Coffee, Snacks & Networking
10:30 – 10:50 | The Age of AI-Driven Continuous Security Validation – Noam Markfeld, VP Sales, Skyhawk Security
Why point-in-time pentests no longer cut it: how AI-based continuous testing and validation defends against AI-driven autonomous attacks, covers third-party risk, and turns security into the live evidence compliance requires.
10:50 – 11:10 | Compliance Trends & The Standards That Matter – Adar Givoni, Director of Customer Services, Scytale
Where compliance is heading and the standards buyers actually ask about – ISO and SOC 2 – closing with GDPR and its Israeli counterpart, Amendment 13.
11:10 – 11:30 | The Value of DPO-as-a-Service – Lior Atias, Fractional CISO & DPO, Cloudride
Why data-protection governance is now a business requirement, and how a fractional DPO gives smaller teams enterprise-grade coverage without the overhead.
11:30 – 11:45 | Interactive Q&A
What You’ll Walk Away With
- Defense against AI-driven attacks – why defensive AI and continuous validation are now table stakes
- A handle on third-party risk – keeping vendor and supply-chain exposure from becoming your weak link
- The standards that actually unlock deals – ISO, SOC 2, GDPR, Amendment 13
- Right-sized governance – staying audit-ready without enterprise overhead