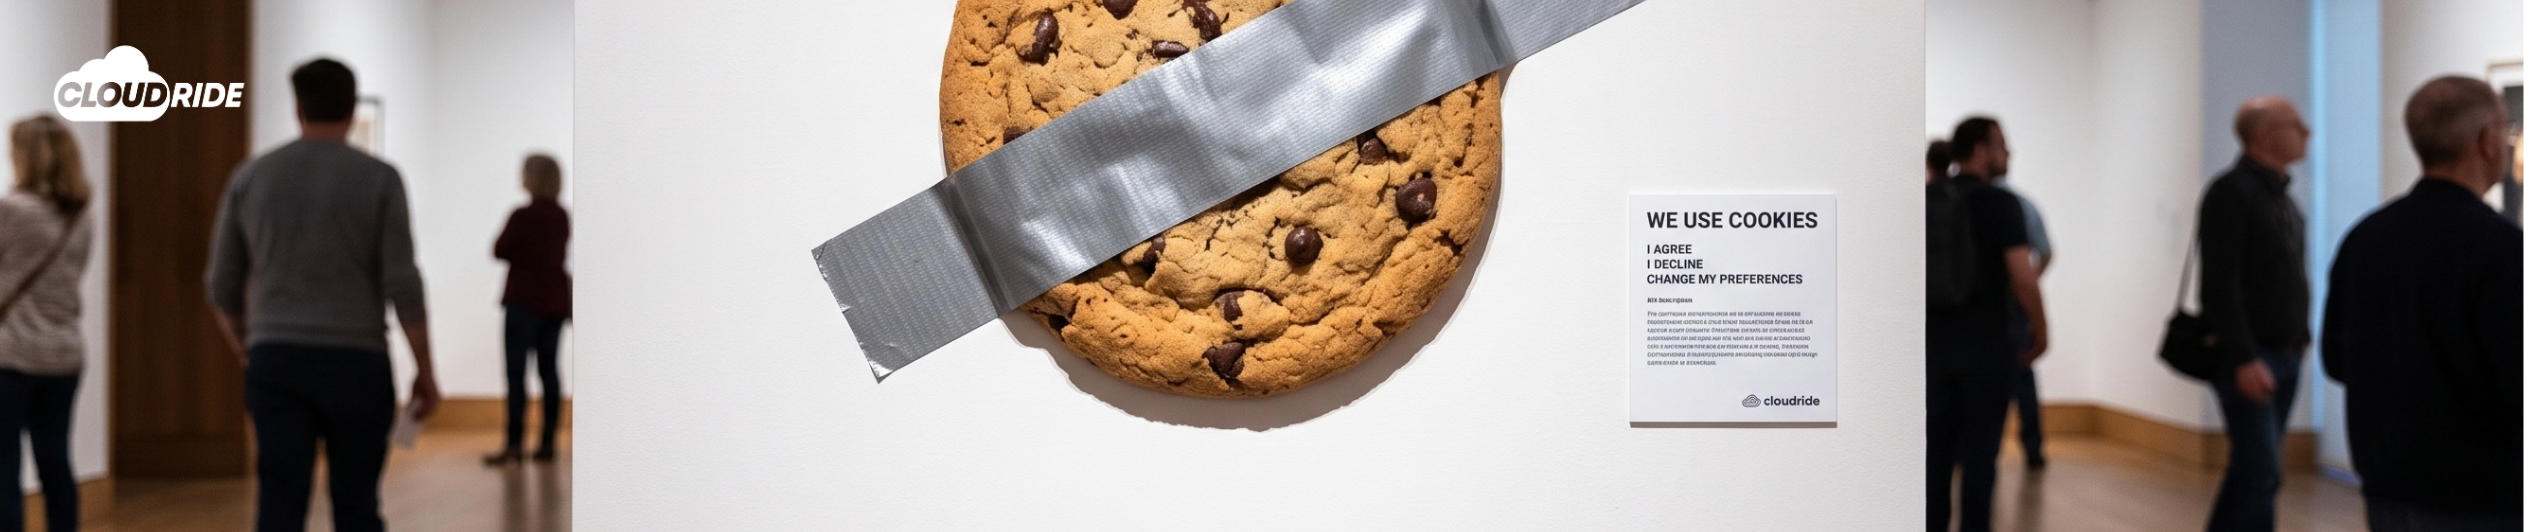
In 2019, Italian artist Maurizio Cattelan duct-taped a fresh banana to a wall at Art Basel Miami, titled it Comedian, and sold it for $120,000.
It sparked a global debate: Is it groundbreaking conceptual art, or just an illusion with a high price tag?
Looking at how many organizations handle web privacy today, I see a strikingly similar phenomenon.
Companies are spending substantial time and money placing a glossy Cookie Banner on their homepage, stepping back, and declaring: “Look, our privacy compliance is complete!”
But much like Cattelan’s banana, a cookie banner sitting on a wall – or a website – is often just a public exhibit. The real question isn’t how your banner looks. It’s whether your backend code actually adheres to data privacy laws.
The Misconception Around Privacy Compliance
Recently, we’ve seen a noticeable rise in regulatory scrutiny, DPO audits, and legal warning letters regarding cookies, tracking pixels, and analytics tools on corporate websites.
Where do organizations make their biggest mistake? They start with the banner UI instead of starting with data privacy governance.
There is a widespread misconception that privacy compliance is purely a design problem. While legal frameworks differ across jurisdictions, data privacy laws across the globe – including Israeli Privacy Protection laws and GDPR guidance – emphasize a core rule:
When data processing relies on consent, that consent must be informed, clear, and freely given.
Having an “Accept All” button isn’t a silver bullet for privacy compliance if users have no real visibility into what they are consenting to – or if tracking scripts fire before the user even clicks a button.
To achieve genuine privacy compliance, every organization and DPO must answer:
- What data is actually being collected?
- Which tools and third-party trackers are harvesting it?
- Where is that data being transmitted, and to whom?
- For what purpose is it processed under data privacy law?
- Can your DPO prove your written privacy policy matches technical reality?
Why Modern Tracking Tools Require Active DPO Governance
Popular integrations – such as Google Analytics, Meta Pixel, LinkedIn Insight Tag, Hotjar, and various marketing tools – do far more than count site visits. They build cross-platform user profiles, transmit data across international borders, and share information with third parties in ways that site owners often don’t fully realize.
This is precisely where the role of a Data Protection Officer (DPO) becomes essential.
A DPO’s job isn’t to pick the color scheme or typography of your cookie banner. A DPO’s job is to ensure strict privacy compliance through rigorous Cookie & Tracker Mapping:
- Audit & Identify: Map every active script, tag, and tracker running on your domain.
- Analyze Data Flow: Determine exact data points collected and target destinations.
- Establish Legal Basis: Match each processing activity with its appropriate legal justification under data privacy laws.
- Align Realities: Ensure your Privacy Policy and Cookie Notice accurately reflect actual technical behavior.
- Verify User Choice: Confirm that user consent choices actually control script execution in real-time.
Code vs. Policy: The Real DPO Audit
Don’t just settle for the list of cookies declared in your static Privacy Policy.
From a DPO perspective, you must open your browser’s developer tools and inspect what scripts are actually loading before and after a user makes their consent choice. More often than not, there is a clear disconnect: the legal document says one thing, the banner says another, and the code executes a third.
For any organization aiming for true privacy compliance, bridging this gap is where static documentation transforms into actual data privacy compliance. Creating a precise DPO tracking matrix:
Tracker | Data Collected | Purpose | Third Parties | Data Location | Opt-In/Opt-Out Mechanism
will expose critical privacy compliance gaps that a standard legal review would never catch.
The 5-Minute DPO Test
True privacy compliance doesn’t start with a pop-up. It starts with data visibility, code-level governance, and active DPO oversight.
Ask your team this week:
If a regulator, auditor, or user asks you tomorrow for a complete list of every tracker running on your website and exactly what data it handles – can your DPO provide an accurate answer within 5 minutes?
Has your organization audited what is actually happening at the code level, or are you relying solely on your written privacy policy?


